
Over time the goal posts inevitably move on the subject of website consent, privacy and compliance, and right now we feel it’s the most complex it has ever been to date.
The first thing I can guarantee you is this area of web site regulation is full of grey areas, overlaps and seems to be designed to send you down an extraordinarily complex rabbit hole, which you may return from … if you’re lucky!
As web designers, we don’t like to get involved with legal requirements, we’re not lawyers, we’re creatives, but more and more we are being drawn into putting time and resource into this area.
The final accountability for website compliance lies solely with the website owner, that’s you. As web designer we handle the technical part of implementing and also give you some good advice.
But, lucky for you, we’ve written a blog post to condense and guide you on the regulations and your obligations.
In this blog post we’re going to focus on two key areas of compliance;
- Cookies / Consent for tracking
- Privacy / Personal data collection
The bottom line
Skip to the links below if you’re short on time
The Importance of Website Compliance
Historically, website compliance wasn’t a big issue. Compliance and regulation simply didn’t exist. You would be hard pushed to see a privacy policy, cookie notice or banner in the 90’s and 2000’s. However, fast forward to the 2020’s and website compliance is no longer optional.
Regulations like the UK GDPR, PECR, and DPA 2018 establish legal standards that website owners must follow to ensure transparency, accountability, and respect for users’ data rights. Ignoring these regulations and standards can result in financial penalties, loss of credibility. Adhering to compliance demonstrates a commitment to data protection and privacy, building a foundation for sustained trust and growth in a digital-first world.
Key regulations and recommendations
The UK GDPR, PECR, DPA 2018, and now the DUAA work together, often overlapping, to protect user data and privacy. Together, these regulations provide a comprehensive framework that website owners must follow to ensure data privacy and compliance.
The DPA 2018 largely mirrors the UK GDPR. UK GDPR covers most of the data protection principles and rights for individuals that the DPA 2018 also addresses.
PECR focuses on more specific areas that UK GDPR and DPA 2018 do not directly cover, such as the rules around electronic marketing and cookies.
The DUAA, passed in 2025, amends both the UK GDPR and PECR rather than replacing them. It introduces a few practical changes, most notably a requirement for websites to offer a direct route for data protection complaints, alongside updates to international data transfer rules. It also touches on newer areas like automated decision-making and a narrower set of pre-approved legitimate interests, though these are unlikely to affect most small business websites.
For most websites, implementing UK GDPR ensures that you’re meeting the core requirements of the DPA 2018.
PECR adds the extra layer needed to ensure compliance with rules around cookies and direct marketing communications (emails).
UK GDPR (General Data Protection Regulation)
Purpose: Protects personal data collection, processing and gives users control over their information.
Responsibilities for Websites:
- Get a lawful basis for collecting data (e.g. consent).
- Allow users to access, correct, or delete their data.
- Keep data secure against breaches.
Our recommendation:
- Ensure your website has a privacy policy, user account access, and clear opt-in forms for data collection.
- Provide access to any logins or services used on or via the website to manage their data.
- Implement secure hosting, SSL certificates, and encryption to protect user data.
PECR (Privacy and Electronic Communications Regulations)
Purpose: Covers electronic communications, including cookies and marketing, where these overlap with personal data.
Responsibilities for Websites:
- Ensure your website has a cookie policy
- Get clear consent for cookies and tracking.
- Ensure marketing emails are opt-in and provide an opt-out.
- Protect user privacy in electronic communications.
Our recommendation:
- Implement a cookie policy in your privacy policy if not handled by your cookie consent banner.
- Implement a cookie consent banner that allows users to opt-in or manage preferences for tracking technologies.
- Use platforms like Mailchimp for marketing emails to ensure users opt-in and can manage their preferences.
DPA 2018 (Data Protection Act 2018)
Purpose: UK-specific supplement to UK GDPR, focusing on enforcement and national-specific data protection rules.
The UK GDPR in general, in relation to websites covers the requirements for DPA 2018. However, special provisions may apply in regards to children’s data protection such as requiring parental consent before processing their data, age verification steps, minimising the data collected, specific data policies and the right to data deletion.
Typical examples of websites this is relevant to are sites involved in: Gaming, E-Learning, Social media platforms, Creative platforms, Sports Clubs.
Our recommendation: Typically our clients won’t require any special actions to comply as it’s generally covered in UK GDPR.
If you are collecting data from children under 13 seek specialist legal compliance advice.
DUAA (Data (Use and Access) Act 2025)
Purpose: A 2025 update to UK data law. It doesn’t replace UK GDPR, PECR, or DPA 2018, it amends and adds to them.
Responsibilities for Websites:
- Provide a way for people to raise a data protection complaint directly with you (not just via the ICO)
- Acknowledge complaints within 30 days and confirm the outcome once investigated
- Where personal data is transferred outside the UK, ensure appropriate safeguards are in place
- If relevant to your business, additional rules apply around automated decision-making and a narrower set of pre-approved legitimate interests
Our recommendation: Have a visible route for complaints (a contact page or form is fine), and check where any tools handling customer data (CRM, email marketing, hosting, analytics) actually store that data. Most small business websites won’t need to act on the automated decision-making or legitimate interest changes.
If your site does anything like automated eligibility checks, scoring, or safeguarding-related processing, seek specialist legal compliance advice.
Just tell me what I need on my website
We recommend everyone has a premium Cookie Banner, it will keep you compliant with the minimal amount of effort and maximum peace of mind.
Our recommended checklist is:
- A Privacy policy with link in your footer
- A Cookie Policy (included within your Privacy policy)
- Create an account with CookieYes (If we are setting up for you, follow this video to create the account as we’ll need your username and password)
- Use a premium cookie banner service (provides clear consent and ability manage cookie preferences)
- Ensure sure any marketing features like newsletters have options to opt-in and manage their preferences
- A way to receive and log data protection complaints, with a 30-day acknowledgment process
Other best practice include:
- Place a privacy link near the forms used to collect data
- Opt for automated scans of your website to search for any changes or updates to cookies (so you don’t have to)
Consider implementing Google Consent V2
NOTE: This is only applicable to sites running Google Ads.
While this is not mandatory in the UK, we do consider you opt for this feature.
The key benefit of using Google Consent Mode v2 is that it helps you comply with privacy laws (like GDPR) while still allowing you to gather important website data for analytics and advertising, even when users decline cookies.
It basically fills in the gaps of data using modelling that you would otherwise lose if users decline to accept cookies.
Important Note: The sole responsibility of ensure a website is compliant lies with the owner of the website. It is important you take professional advice and ensure you regularly audit and maintain your consent and privacy obligations.
Are there any costs?
There maybe some costs involved. These could extend to
- Reviewing your existing site
- Setting up your site with a new cookie banner
- Setting up Google consent mode V2
- Upgrading your cookie banner service to handle automated scanning of your cookies (so you don’t have to)
All sites are different, so there’s no one size-fits-all cost.
Typically though, we’d estimate in the region of 1 to 2 hours of our time for most clients sites (at our standard hourly rate)
and for most sites the free service from Cookie Yes will suffice, however if you want to automate the scanning of cookies to ensure you are always compliant then you will require their paid Pro service which is currently $25 per month
Is their any ongoing maintenance needed?
Typically, we would recommend you login to your Cookie Yes account every month and click a single button to scan your website for any updates to cookies.
Cookies can change from time to time.
If you opt for
Of course, you need to occasional ensure your privacy policy is up to date and compliant.
and finally, if you add or update any features on your site like newsletters for example, you need to ensure these are inline with the UK GDPR and PECR regulations.
Are premium cookies banner free?
Yes and No.
All premium cookies banners generally offer a free entry level. This will usually have a limit on the number of pages on your site, the amount those pages are viewed and the automation of cookie scanning.
For most sites, the cookie banner will be free.
For sites with more than around 100 pages or 15,00 page views per month or want the automated cookie scanner feature, this will attract a small monthly costs, around $25pm.
Will my existing cookie banner and policies be compliant?
It depends.. is the short answer.
The best answer though is to upgrade your site to a newer compliant cookie banner and policy.
Lots of our older sites came with a simple cookie banners and or a privacy policy link in the website footer. Many look similar to the example below.

In many cases, sites with this could still be considered compliant. If your site only uses strictly necessary cookies.
You can check your site here to find out: https://www.cookieyes.com/cookie-checker/
If the results only show the cookie types as necessary, as show in the example below, it’s likely you don’t need a cookie banner at all, only a privacy policy in the footer. However, that could change in time.
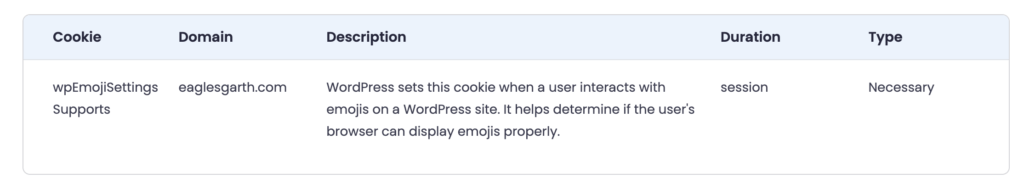
As for the privacy policy, this could need updating, or replacing.
You can request a copy of our generic template policy by contacting us, or you can create a generic privacy policy using the cookie banner service from Cookie Yes.
Answers to common questions
Privacy
Is it mandatory to have a privacy Policy?
Yes, it is mandatory in the UK to have a privacy policy on a website if you collect, process, or store personal data about your website visitors, customers, or users.
Here’s why; Legal Basis
UK General Data Protection Regulation (UK GDPR)
The UK GDPR requires businesses to be transparent about how they handle personal data. A privacy policy is the primary method for providing this information.
Personal data includes names, email addresses, IP addresses, and any other information that can identify an individual.
Data Protection Act 2018
This act works alongside the UK GDPR to enforce data protection laws in the UK. A privacy policy ensures compliance with the law’s requirements for transparency and accountability.
Privacy and Electronic Communications Regulations (PECR)
If your website uses cookies or similar technologies to track user behavior, the Privacy and Electronic Communications Regulations (PECR) mandate you inform users and obtain their consent. A privacy policy typically outlines these details.
Are there any exemptions?
You might not need a privacy policy if:
No Personal Data Collection:
- Your website does not collect any form of personal data (e.g., through forms, cookies, analytics, or accounts)
Purely Personal Use:
- A website operated purely for private, non-commercial use may not fall under GDPR requirements.
However.. Even if you think you don’t collect personal data, it’s worth noting that many modern websites inadvertently collect some (e.g., IP addresses through analytics tools or server logs). Therefore, it’s safer to have a privacy policy in place.
What should a privacy policy include?
A compliant privacy policy should explain:
- What data you collect.
- Why you collect it.
- How it will be used.
- Who it will be shared with.
- How long it will be retained.
- The legal basis for processing the data.
- Users’ rights regarding their data.
- How to raise a data protection complaint, and how it will be handled.
Do I have to update my privacy policy with the exact cookies if they change?
Under UK GDPR and PECR (Privacy and Electronic Communications Regulations), you are required to provide users with accurate and up-to-date information about the cookies you use.
There is no specific timeframe mandated by UK GDPR or PECR for how often you must audit your website to ensure your privacy and cookie policy matches your site’s practices. However, both regulations require you to keep your information accurate and up to date, which implies regular auditing is necessary.
Is having a Privacy policy link in the footer of my website acceptable?
Yes, it is generally acceptable under the UK GDPR for a website to place its privacy policy link in the footer, as long as it is clearly visible and accessible from all pages of the site. This is a common practice and aligns with the principle of transparency, as long as:
The link is clearly labeled: For example, it should be titled “Privacy Policy,” “Data Protection,” or something similarly unambiguous.
The link is easy to find: Users should not have to hunt for the policy. Placing it in the footer is considered standard and acceptable if the footer is always accessible.
The content of the privacy policy is clear and comprehensive: It should inform users about how their data is collected, used, and stored, in compliance with GDPR requirements.
It’s accessible before consent is given: If a website collects personal data (e.g., through cookies or sign-up forms), users must have access to the privacy policy before they agree to provide any data or consent to cookie use.
While placing the link in the footer is widely accepted, for key points like cookie consent, many sites supplement this by providing direct links to the privacy policy in consent banners or pop-ups to ensure users can easily access it.
Do I need a complaints process on my website?
Yes. Since June 2026, UK law (the Data (Use and Access) Act 2025) requires all organisations processing personal data to have a way for people to raise a complaint directly with you, not just via the Information Commissioner’s Office (ICO). This means acknowledging complaints within 30 days and confirming the outcome once investigated.
Cookies
Is it mandatory to have a cookie banner?
Yes, having a cookie banner or notice is often mandatory under the EU General Data Protection Regulation (GDPR) and the Privacy and Electronic Communications Regulations (PECR) if your website uses cookies or similar tracking technologies that process personal data.
Here’s what you need to know: When is a Cookie Banner Mandatory?
Under GDPR
- If cookies are used to process personal data (e.g., IP addresses, device identifiers), you must have user consent before setting those cookies, except for strictly necessary cookies.
Under PECR
- PECR requires user consent before storing or accessing information (like cookies) on a user’s device, regardless of whether the cookies involve personal data.
Non-Compliance Risks
- Fines can be significant under GDPR (up to £17.5 million or 4% of global turnover).
- Under PECR, regulators like the ICO in the UK can issue fines for not obtaining consent before setting cookies.
Is my website exempt from having a cookie banner?
“Strictly necessary” cookies don’t require consent under PECR but must be transparently disclosed under UK GDPR.
For strictly necessary cookies, including a link to your cookie policy in the footer of the website, where you provide clear and detailed information about the cookies in use, is generally sufficient for UK GDPR compliance.
There is no need for a cookie consent banner or pop-up, as long as users are informed and the cookies are essential for the site’s operation.
Since necessary cookies don’t require consent, a banner is not mandatory. Just ensuring that users can access the relevant information about cookies via the footer or cookie policy meets the transparency obligation.
However… Most sites use features like website forms, spam reduction services, Google Maps and the like. If you are using these you’ll need a compliant cookie banner.
What are examples of strictly necessary cookies?
Strictly necessary cookies are essential for a website to function properly and cannot typically be disabled by the user without impairing the website’s functionality.
These cookies are usually first-party and exempt from user consent requirements under most privacy regulations, as they are critical for the website to work correctly.
Here are some common examples:
Session Cookies: Maintain the user’s session across different pages of a website, ensuring that login or form submissions persist as users navigate.
Authentication Cookies: Verify the identity of logged-in users to grant them access to secure areas, such as a dashboard or account settings.
Shopping Cart Cookies: Store items added to a shopping cart on e-commerce websites.
Payment Gateway Cookies: Enable secure payments by maintaining session integrity during the checkout process.
Security Cookies: Detect and prevent security threats like unauthorized logins or Cross-Site Request Forgery (CSRF).
Load Balancing Cookies: Direct traffic to different servers to optimize performance and ensure reliability during high traffic periods.
User Consent Cookies: Remember user preferences for cookie consent settings to comply with regulations like GDPR or CCPA.
Form State Cookies: Prevent loss of form data when navigating between pages or refreshing.
Language Preference Cookies: Store the user’s preferred language or regional settings for consistent browsing.
Subscription Service Cookies: Manage access to paid or restricted content based on subscription level or account status.
What should a cookie banner include?
The Privacy and Electronic Communications Regulations (PECR) govern the use of cookies and similar technologies in the UK.
PECR requirements are enforced alongside UK GDPR, which emphasizes transparency and accountability, ensuring users’ personal data is handled appropriately.
If your website uses cookies, you must comply with the following requirements:
Inform Users About Cookies
- You must provide clear and comprehensive information about the cookies used on your site.
- This includes detailing:
- What the cookies are for.
- Who sets them (first-party or third-party cookies).
- How long the cookies will remain active.
Obtain Consent Before Storing Cookies
- You must get prior consent before storing or accessing cookies on a user’s device unless the cookie is strictly necessary.
- Consent must be:
- Informed: Users must understand what they’re agreeing to.
- Freely given: Users must have a real choice to accept or reject cookies.
- Unambiguous: There should be an explicit action, like clicking “Accept.” Pre-ticked boxes do not count as valid consent.
Strictly Necessary Cookies Are Exempt
- You don’t need consent for cookies that are strictly necessary to provide a service requested by the user (e.g., remembering items in a shopping cart or session cookies for security).
Allow Users to Refuse Cookies
- Users must have the option to reject non-essential cookies just as easily as accepting them.
- This should be part of the initial interaction with the cookie banner or pop-up, not hidden in complex settings.
Enable Withdrawal of Consent
- Users must be able to withdraw their consent easily at any time (e.g., through a “Manage Cookies” option on your cookie banner).
Link to Detailed Cookie Policy
- Include a link to your full cookie policy, which should explain:
- What types of cookies are used.
- Who sets the cookies (e.g., your business or third parties).
- How long cookies are stored.
- Instructions for withdrawing consent.
About Google Consent Mode V2
If you use Google Ads, Google Analytics, or Google Tag Manager then Google Consent Mode V2 it is necessary for compliance with the UK GDPR and PECR when collecting data via these tools.
Consent Mode helps ensure that Google’s tracking technologies respect users’ consent choices, especially in relation to analytics and marketing cookies.
Google Consent Mode works with Google other products to adjust tracking based on user consent. For instance, if a user declines marketing cookies, it will prevent advertising-related data from being collected, while still allowing analytics data collection if permitted.
It’s important to configure this mode correctly to ensure that all third-party tracking tools, like Google Tag Manager, respect user consent.
This information is provided for general guidance only and does not constitute legal advice. Given the evolving nature of consent and privacy regulations, as well as changes in available tools and methods, the recommendations provided may be subject to change. We strongly recommend consulting with a compliance or legal professional to ensure full compliance with applicable laws.
